
Operate across regulated
environments with clearer
controls, evidence and
accountability.
Zoiko Tech supports organizations operating under material regulatory, security, privacy, identity and governance requirements by connecting obligations, controls, evidence and accountable workflows — while keeping jurisdiction, operator and claim boundaries explicit.
Jurisdiction-aware. Evidence-led. Operator-clear. Human-accountable.
Start with your sector and jurisdiction
These inputs route you to the right industry, solution and trust context. They never determine
which laws or controls apply to you.

Industry

Country / region / jurisdiction

Organization / operator type

Regulated activity

Environment
Where do you need to start?
Six requirement areas, each routed to the right page.

Regulatory obligations /
controls
Connect obligations, control ownership, evidence and reviewable workflows.
Regulatory & Compliance

Identity / authority
Authenticate people and systems and control delegated authority.
Identity & Access
Cybersecurity / resilience
Protect systems, users and continuity; understand incident and status evidence.
Cybersecurity & Resilience / Trust Center
AI governance / assurance
Govern AI systems, agents, evidence, human oversight and approvals.
AI Governance & Assurance /Responsible AI

Developer / integration controls
Integrate regulated workflows without losing identity, provenance or observability.
Modernization & Integration /Developer Platform

Privacy / data governance
Control purpose, access, minimization and approved data use.
Privacy / Trust CenterPriority regulated-operating problems
Obligations sit apart from
operationsCompliance becomes spreadsheet-driven and hard to trace.
Route: Regulatory & ComplianceIdentity and authority are
ambiguousRegulated actions may need explicit person, system or representative authority.
Route: Identity & AccessSecurity and privacy proof
is disconnectedControls are hard to verify without authoritative evidence.
Route: Trust Center, Security, PrivacyAI raises new
accountability questionsAgents and models may need human oversight, evaluation and bounded authority.
Route: AI Governance & Assurance
Obligation, control and evidence
architecture
Seven layers from who is in scope to whether the control stays current and reviewable.
- L1
Sector, entity and activity
The actual economic sector,
legal or commercial operator and
regulated activity at approved
scope.Who or what is in scope?
- L2
Jurisdiction and source
Authoritative law, regulation,
policy, standard, contract or
internal source where supported.What requirement is authoritative?
- L3
Obligation / requirement
Structured requirement or
responsibility at approved
product and legal scope.What must be done or demonstrated?
- L4
Control / workflow
Technical, procedural or
operational control with an
owner and system or process.How is the requirement
operationalized? - L5
Identity, approval,
exceptionWho may act, review, approve or
override, plus exception and
remediation state.Who owns the decision?
- L6
Evidence / assurance
Evidence object, source,
freshness, scope, reviewer and
any claim or certification
relationship.What proves the control operates?
- L7
Monitoring, change, audit
Changes, expiry, incidents,
control failures, audit history and
re-review.Can it stay current and reviewable?
Regulatory and compliance workflows
Six objects, each with an owner, state and review path.
Obligation / requirement
Source, jurisdiction or scope,
effective period, owner and state
where approved.Control
Control type, responsible owner,
implementation and evidence
state, and exceptions.Evidence
Source, period, freshness,
scope, reviewer and linked
control or claim.Exception
Reason, impact where approved,
owner, remediation or
compensating control, review
date.Approval / sign-off
Authorized role, scope,
conditions and time.Change event
A source, rule, product or market
change that triggers re-review.
Identity and delegated authority
Regulated actions need clear authority. Identity is described only at the scope products
support.
Person identity
Authentication or verification
only at product-supported
scope. No inferred assurance
level or certification.Workforce / regulated role
Role, organization, environment
and function as approved.
Professional or licensed status
only if authoritative.External / vendor identity
Explicit organization, contract
and scope boundary.Delegated authority
Representative, approver, agent
or service-provider authority,
explicit and revocable where
supported.System / service identity
Machine identity and
authorization where supported.Audit
Material access, delegation and
approval events where the
product supports them.
Security, privacy and resilience
Security
Secure engineering, least
privilege, threat prevention and
authoritative security evidence.Privacy
Purpose limitation, data
minimization and privacy-
conscious architecture.Reliability / resilience
Observability, status
communication, operational
controls and recovery evidence.Incident / disclosure
Authoritative Support, Status and
Responsible Disclosure routes.Data / jurisdiction
No sovereign, in-country or
regulated-hosting claim without
exact deployment evidence.Third parties
Provider, subprocessor and
integration evidence only from
approved sources.
AI governance and assurance
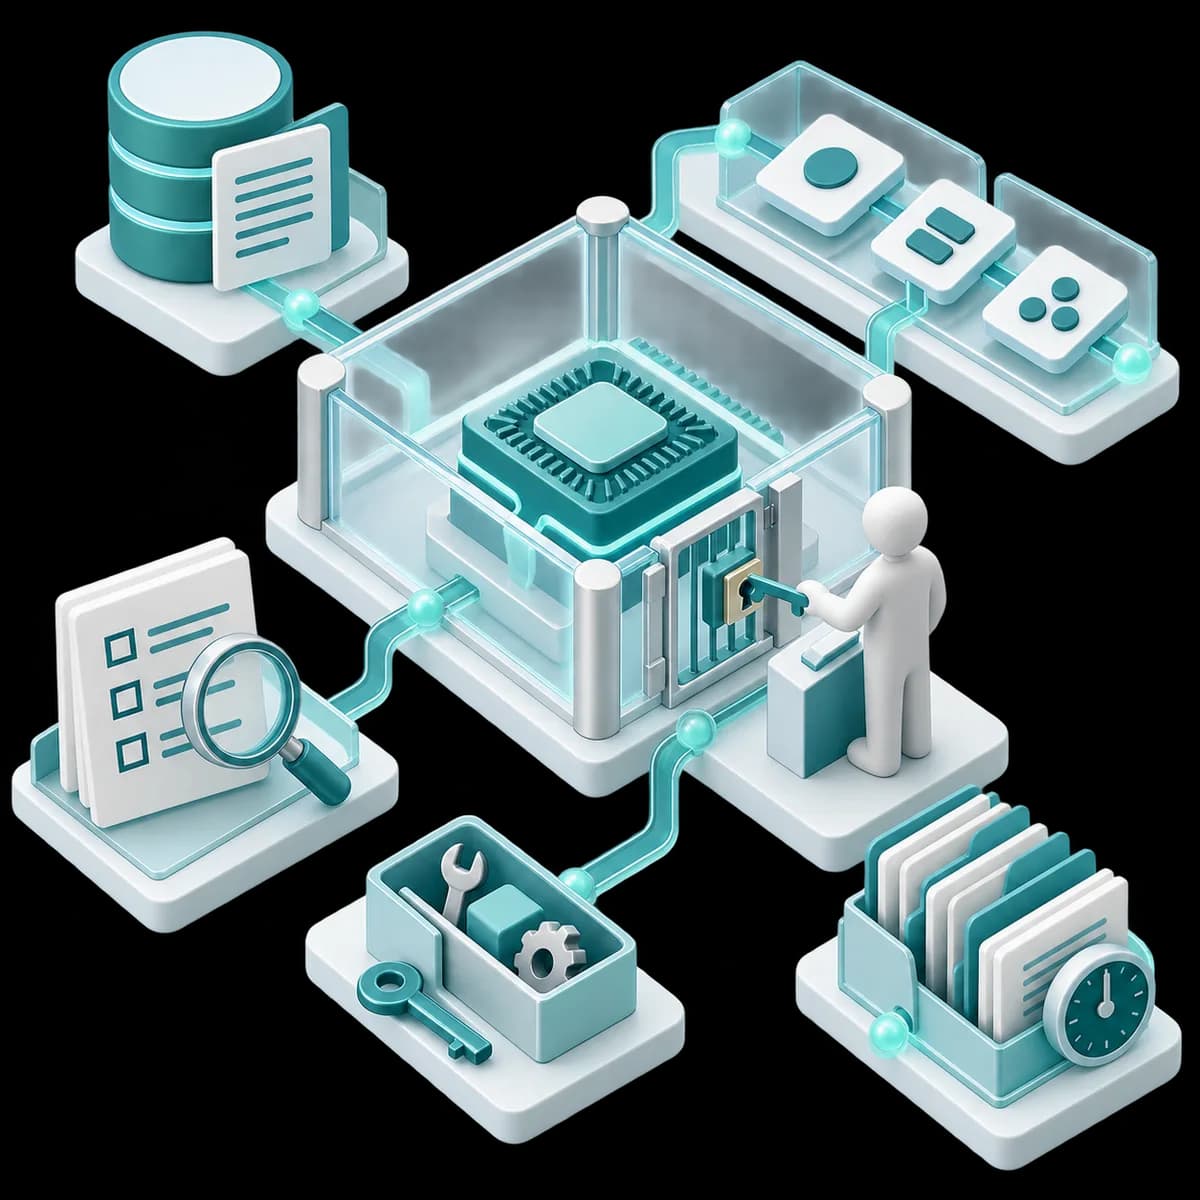
AI in regulated settings stays bounded, reviewable and human-accountable.

Inventory / use case
AI system, agent or workflow
context, purpose and owner at
supported scope.
Authority mode
Assist, recommend, prepare,
execute with approval. Bounded
execution only where approved.
Human oversight
A named accountable reviewer
or approver for material
decisions.
Evaluation
Approved test evidence,
limitations and review date.
Agent / tool permissions
Explicit system, data and action
scope. No self-expanding
authority.
Evidence / audit
Source, model, policy, approval
and action evidence where
supported.
Jurisdiction, market and operator truth
Six facts we state precisely, or not at all.
Legal / commercial
operatorThe exact entity operating or
contracting for the platform or
service, where material.Markets / availability
Only locations and markets
actually approved in the product
registry.Regulated status
Licensing, authorization and
regulated-service wording from
a controlled compliance source.Jurisdiction context
Relevant jurisdiction only when
authoritative and materially
applicable.Deployment
Cloud, hybrid, on-premises,
region or residency only when
deployment evidence supports it.Group platform attribution
Sector-owned or Group
platforms are never shown as
Zoiko Tech-operated when they
aren’t.
Certification, attestation and claims
A five-level hierarchy. Each level looks different on purpose, so a weaker claim never passes
for a stronger one.
Certified / Attested
Exact external certificate, attestation or assurance artifact
with scope, entity, issuer and expiry.Rule: exact approved wording only.
Compliant
A legal or compliance-approved statement with defined
scope.Rule: only where legally verified.
Aligned / Designed to
Architecture or control intent or alignment. Not certification.
Rule: never styled like a certified or compliant badge.
Roadmap / Target
Future intent or target.
Rule: clearly future-looking, no present-tense claim.
Unknown / Not claimed
No approved evidence or wording.
Rule: hide the claim or state “not claimed.” Never interpolate.
Evidence and audit lifecycle
Every evidence record carries the same eight fields.

Evidence ID
Stable internal identifier.

Type
Control evidence, certification or
attestation, policy, audit or
assessment, operational
evidence, customer proof.
Source / owner
Authoritative source and
accountable owner.
Scope
Entity, product, control, system,
market or jurisdiction and period
as relevant.
State
Draft, Under review, Approved,
Published, Expired, Withdrawn,
Superseded.
Freshness
Valid from, review by, and expiry
where applicable.
Allowed wording
Exact public claim language if
the evidence backs a marketing
or trust claim.
Linked claims / controls
Only approved relationships.
Platform and technology evidence
Candidate platforms appear only when public destination, scope, maturity and claims are
approved. Missing operator, maturity, regulated status or evidence means the card isn’t
shown.
Zoiko Assure
Technology and assurance
Build · hidden until approved
destination candidate.Zoiko iD
Digital identity and access
Build · hidden until approved
technology candidate. No
assurance levels or protocols
without product evidence.Zoiko Access
Industry solution candidate, once
Build · hidden until approved
sector and use-case scope is
defined.ZoikoTax
Specialist tax and regulatory
Build · hidden until approved
solution candidate. No tax
advice, filing authority or
jurisdiction coverage implied.Zoikorum
Regulated and professional-
Build · hidden until approved
services candidate. No licensed
service or legal representation
implied.CoreX
Shared control, evidence and
Build · public only if approved
transaction infrastructure, when
customer-facing.Zoiko AI
Governed agentic intelligence
architecture. Approved AI
governance and regulated-use
patterns only.Live enterprise platforms
ZoikoNex, Time, HR, Payroll,
A live product doesn’t imply
Billing, Local, Sema and others
as workflow evidence within
approved scope.
certification or jurisdictional
suitability.
Integration and developer layer
Build
Developer Platform, approved
APIs, SDKs, model APIs,
webhooks and events,
authentication.Learn
Documentation, API reference,
quickstarts, architecture guides.Test
Sandbox, samples and reference
implementations only when
external self-service is live.Operate
Observability, status, usage and
metering where available,
changelog, developer support.
Implementation and control adoption

Define sector, activity,
jurisdictionCanonical industry,
Scope approved
legal or commercial
entity, regulated activity
and target outcome.
Identify authoritative
requirementsMap authoritative
Requirement set approved
sources with authorized
legal and compliance
review.
Map identity, systems,
controlsOwners, systems of
Control architecture
record, identities,
delegated authority,
controls and evidence
sources.
approved
Define claims and
evidence boundariesWhich claims need
Claims model approved
certification,
compliance or
alignment wording and
approved evidence.
Integrate / configure
Connect APIs, events
Technical design approved
and workflows without
losing source, authority,
operator or jurisdiction
metadata.
Validate exceptions
and failuresMissing evidence,
Acceptance criteria met
expired certification,
unsupported market,
access failure, control
exception, AI-review
states.
Pilot
A bounded regulated
Pilot reviewed
workflow using
controlled or synthetic
data where possible.
Operate, monitor, re-
reviewEvidence freshness,
Operational readiness
control exceptions,
product and regulatory
change, approval
expiry.
maintained
Technology in practice
Proof appears only when approved for public use.
Regulatory workflow
Obligation and operational
Evidence pending
problem, control architecture,
deployment, approved
measurable result, evidence and
permission.Identity / authority
Authority or access problem,
Evidence pending
delegated-control architecture,
approved operational result.Security / resilience
Risk or operational challenge,
Evidence pending
control architecture, approved
outcome, without overstated
certification.AI governance
Bounded AI use case, evaluation,
Evidence pending
human oversight, approval,
approved result and limitations.
Customer evidence contract
What any customer story must meet before it’s published.
Customer identity
Only with explicit legal and
customer approval.Regulated context
Approved sector, jurisdiction and
workflow scope only. No
confidential or supervisory
detail.Problem
A concrete operational problem
without privileged or regulated
confidential data.Deployment
Actual approved technology,
operator, environment and
integration scope.Result
Only measured, Evidence-
Registry-backed outcomes.Regulatory wording
Legal and compliance review
required. No implied certification
or authorization beyond
evidence.Visuals
Approved real interface,
architecture or imagery, or
clearly marked specimen.
Buyer questions, answered directly
The footer uses this label as a discovery route for organizations operating under material
regulatory, security, privacy, identity or governance constraints. The supplied sources don’t
define it as a separate canonical economic-sector taxonomy.
Modernize regulated operations without
hiding jurisdiction, authority or evidence
boundaries.
Talk with Zoiko Tech about the sector, jurisdictions, regulated activities, systems and control
or evidence requirements you need to support. We’ll route the discussion to the relevant
industry, solution, technology and trust context.
Operate across regulated
environments with clearer
controls, evidence and
accountability.
Zoiko Tech supports organizations operating under material regulatory, security,
privacy, identity and governance requirements by connecting obligations, controls,
evidence and accountable workflows — while keeping jurisdiction, operator and
claim boundaries explicit.
Jurisdiction-aware. Evidence-led. Operator-clear. Human-accountable.
jurisdiction
policy source
authority
workflow
regulated operating context. Zoiko Tech’s Industries remain true economic sectors, and no
separate list of “regulated sectors” is created here.
Start with your sector and jurisdiction
These inputs route you to the right industry, solution and trust context. They never
determine which laws or controls apply to you.
controls apply based on industry, country, company size or activity. Anything we can’t
confirm from an approved source reads “Requires review.” Your context carries into the
Contact Sales and solution routes in privacy-safe form.
Where do you need to start?
Six requirement areas, each routed to the right page.
- Regulatory obligations / controlsConnect obligations, control ownership,
evidence and reviewable workflows.Regulatory & Compliance - Identity / authorityAuthenticate people and systems and
control delegated authority.Identity & Access - Cybersecurity / resilienceProtect systems, users and continuity;
understand incident and status
evidence.Cybersecurity & Resilience / Trust Center - Privacy / data governanceControl purpose, access, minimization
and approved data use.Privacy / Trust Center - AI governance / assuranceGovern AI systems, agents, evidence,
human oversight and approvals.AI Governance & Assurance / Responsible AI - Developer / integration controlsIntegrate regulated workflows without
losing identity, provenance or
observability.Modernization & Integration / Developer
Platform
Priority regulated-operating problems
Obligations sit apart from
operationsCompliance becomes spreadsheet-
Route: Regulatory & Compliance
driven and hard to trace.Identity and authority are
ambiguousRegulated actions may need explicit
Route: Identity & Access
person, system or representative
authority.Security and privacy proof is
disconnectedControls are hard to verify without
Route: Trust Center, Security, Privacy
authoritative evidence.AI raises new accountability
questionsAgents and models may need human
Route: AI Governance & Assurance
oversight, evaluation and bounded
authority.
Obligation, control and evidence
architecture
Seven layers from who is in scope to whether the control stays current and reviewable.
 L1
Sector, entity and activity
The actual economic sector, legal or
Who or what is in scope?
commercial operator and regulated
activity at approved scope. L2
Jurisdiction and source
Authoritative law, regulation, policy,
What requirement is authoritative?
standard, contract or internal source
where supported. L3
Obligation / requirement
Structured requirement or responsibility
What must be done or demonstrated?
at approved product and legal scope. L4
Control / workflow
Technical, procedural or operational
How is the requirement operationalized?
control with an owner and system or
process. L5
Identity, approval, exception
Who may act, review, approve or
Who owns the decision?
override, plus exception and remediation
state. L6
Evidence / assurance
Evidence object, source, freshness,
What proves the control operates?
scope, reviewer and any claim or
certification relationship. L7
Monitoring, change, audit
Changes, expiry, incidents, control
Can it stay current and reviewable?
failures, audit history and re-review.
legal conclusion is never generated from generic AI, marketing copy or an unverified system
state. We route to authoritative sources and show Unknown or Requires review when scope
is insufficient.
Regulatory and compliance workflows
Six objects, each with an owner, state and review path.
Obligation / requirement
Source, jurisdiction or scope, effective
period, owner and state where
approved.Control
Control type, responsible owner,
implementation and evidence state, and
exceptions.Evidence
Source, period, freshness, scope,
reviewer and linked control or claim.Exception
Reason, impact where approved, owner,
remediation or compensating control,
review date.Approval / sign-off
Authorized role, scope, conditions and
time.Change event
A source, rule, product or market
change that triggers re-review.
Identity and delegated authority
Regulated actions need clear authority. Identity is described only at the scope products
support.
Person identity
Authentication or verification only at
product-supported scope. No inferred
assurance level or certification.Workforce / regulated role
Role, organization, environment and
function as approved. Professional or
licensed status only if authoritative.External / vendor identity
Explicit organization, contract and scope
boundary.Delegated authority
Representative, approver, agent or
service-provider authority, explicit and
revocable where supported.System / service identity
Machine identity and authorization
where supported.Audit
Material access, delegation and approval
events where the product supports
them.
when ready. No MFA, SSO, SCIM, passwordless, identity proofing, entitlement, regulated
assurance level or government or industry identity compliance is claimed without dedicated
product evidence.
Security, privacy and resilience
Security
Secure engineering, least privilege,
threat prevention and authoritative
security evidence.Privacy
Purpose limitation, data minimization and
privacy-conscious architecture.Reliability / resilience
Observability, status communication,
operational controls and recovery
evidence.Incident / disclosure
Authoritative Support, Status and
Responsible Disclosure routes.Data / jurisdiction
No sovereign, in-country or regulated-
hosting claim without exact deployment
evidence.Third parties
Provider, subprocessor and integration
evidence only from approved sources.
AI governance and assurance
AI in regulated settings stays bounded, reviewable and human-accountable.
Inventory / use case
AI system, agent or workflow context,
purpose and owner at supported scope.Authority mode
Assist, recommend, prepare, execute
with approval. Bounded execution only
where approved.Human oversight
A named accountable reviewer or
approver for material decisions.Evaluation
Approved test evidence, limitations and
review date.Agent / tool permissions
Explicit system, data and action scope.
No self-expanding authority.Evidence / audit
Source, model, policy, approval and
action evidence where supported.High-impact use
No implied autonomous regulated, legal,
eligibility, clinical, financial or
enforcement decisions without separate
approval.
Jurisdiction, market and operator truth
Six facts we state precisely, or not at all.
Legal / commercial operator
The exact entity operating or contracting
for the platform or service, where
material.Markets / availability
Only locations and markets actually
approved in the product registry.Regulated status
Licensing, authorization and regulated-
service wording from a controlled
compliance source.Jurisdiction context
Relevant jurisdiction only when
authoritative and materially applicable.Deployment
Cloud, hybrid, on-premises, region or
residency only when deployment
evidence supports it.Group platform attribution
Sector-owned or Group platforms are
never shown as Zoiko Tech-operated
when they aren’t.
Certification, attestation and claims
A five-level hierarchy. Each level looks different on purpose, so a weaker claim never
passes for a stronger one.
Certified / Attested
Exact external certificate,
attestation or assurance
artifact with scope, entity,
issuer and expiry.Rule: exact approved
wording only.Compliant
A legal or compliance-
approved statement with
defined scope.Rule: only where legally
verified.Aligned / Designed to
Architecture or control
intent or alignment. Not
certification.Rule: never styled like a
certified or compliant
badge.Roadmap / Target
Future intent or target.
Rule: clearly future-looking,
no present-tense claim.Unknown / Not claimed
No approved evidence or
wording.Rule: hide the claim or state
“not claimed.” Never
interpolate.
Badge rule. No certification-style seals, checkmarks or regulator logos for Aligned, Designed
to or Roadmap claims.
Evidence and audit lifecycle
Every evidence record carries the same eight fields.
Evidence ID
Stable internal identifier.
Type
Control evidence, certification or
attestation, policy, audit or assessment,
operational evidence, customer proof.Source / owner
Authoritative source and accountable
owner.Scope
Entity, product, control, system, market
or jurisdiction and period as relevant.State
Draft, Under review, Approved,
Published, Expired, Withdrawn,
Superseded.Freshness
Valid from, review by, and expiry where
applicable.Allowed wording
Exact public claim language if the
evidence backs a marketing or trust
claim.Linked claims / controls
Only approved relationships.
- Draft
- Under review
- Approved
- Published
- Expired
- Withdrawn
- Superseded
Platform and technology evidence
Candidate platforms appear only when public destination, scope, maturity and claims are
approved. Missing operator, maturity, regulated status or evidence means the card isn’t
shown.
Zoiko Assure
Technology and assurance destination
Build · hidden until approved
candidate.Zoiko iD
Digital identity and access technology
Build · hidden until approved
candidate. No assurance levels or
protocols without product evidence.Zoiko Access
Industry solution candidate, once sector
Build · hidden until approved
and use-case scope is defined.ZoikoTax
Specialist tax and regulatory solution
Build · hidden until approved
candidate. No tax advice, filing authority
or jurisdiction coverage implied.Zoikorum
Regulated and professional-services
Build · hidden until approved
candidate. No licensed service or legal
representation implied.CoreX
Shared control, evidence and
Build · public only if approved
transaction infrastructure, when
customer-facing.Zoiko AI
Governed agentic intelligence
architecture. Approved AI governance
and regulated-use patterns only.Live enterprise platforms
ZoikoNex, Time, HR, Payroll, Billing,
A live product doesn’t imply certification or
Local, Sema and others as workflow
evidence within approved scope.
jurisdictional suitability.
Evidence-card contract. Canonical name, approved descriptor, maturity, legal or commercial
operator, market or jurisdiction where material, regulated or certification status, evidence
link, limitations and CTA.
Integration and developer layer
Build
Developer Platform, approved APIs,
SDKs, model APIs, webhooks and
events, authentication.Learn
Documentation, API reference,
quickstarts, architecture guides.Test
Sandbox, samples and reference
implementations only when external
self-service is live.Operate
Observability, status, usage and
metering where available, changelog,
developer support.Regulated integration
Identity, evidence, control, workflow and
system-of-record integrations only when
current documentation supports them.
No integrations are implied with regulators, government registries, KYC / AML or sanctions
providers, healthcare exchanges, banking rails, tax authorities, justice systems, certification
bodies or regulated cloud frameworks unless current approved documentation supports
them.
Implementation and control adoption
Define sector,
activity, jurisdictionCanonical industry,
Scope approved
legal or commercial
entity, regulated activity
and target outcome.Identify authoritative
requirementsMap authoritative
Requirement set approved
sources with authorized
legal and compliance
review.Map identity,
systems, controlsOwners, systems of
Control architecture
record, identities,
delegated authority,
controls and evidence
sources.
approvedDefine claims and
evidence boundariesWhich claims need
Claims model approved
certification,
compliance or
alignment wording and
approved evidence.Integrate / configure
Connect APIs, events
Technical design approved
and workflows without
losing source, authority,
operator or jurisdiction
metadata.Validate exceptions
and failuresMissing evidence,
Acceptance criteria met
expired certification,
unsupported market,
access failure, control
exception, AI-review
states.Pilot
A bounded regulated
Pilot reviewed
workflow using
controlled or synthetic
data where possible.Operate, monitor, re-
reviewEvidence freshness,
Operational readiness
control exceptions,
product and regulatory
change, approval
expiry.
maintained
Technology in practice
Proof appears only when approved for public use.
Regulatory workflow
Obligation and operational problem,
Evidence pending
control architecture, deployment,
approved measurable result, evidence
and permission.Identity / authority
Authority or access problem, delegated-
Evidence pending
control architecture, approved
operational result.Security / resilience
Risk or operational challenge, control
Evidence pending
architecture, approved outcome, without
overstated certification.AI governance
Bounded AI use case, evaluation, human
Evidence pending
oversight, approval, approved result and
limitations.
No approved regulated-domain proof yet? See the architecture, claims hierarchy, Trust,
Security, Privacy and Responsible AI routes, or contact sales. We don’t publish regulatory
approvals, certifications, audit results, fines avoided, compliance percentages, customer
logos, regulator names or market coverage.
Customer evidence contract
What any customer story must meet before it’s published.
Customer identity
Only with explicit legal and customer
approval.Regulated context
Approved sector, jurisdiction and
workflow scope only. No confidential or
supervisory detail.Problem
A concrete operational problem without
privileged or regulated confidential data.Deployment
Actual approved technology, operator,
environment and integration scope.Result
Only measured, Evidence-Registry-
backed outcomes.Regulatory wording
Legal and compliance review required.
No implied certification or authorization
beyond evidence.Visuals
Approved real interface, architecture or
imagery, or clearly marked specimen.
Buyer questions, answered directly
The footer uses this label as a discovery route for organizations operating under material
regulatory, security, privacy, identity or governance constraints. The supplied sources
don’t define it as a separate canonical economic-sector taxonomy.
Modernize regulated operations without
hiding jurisdiction, authority or evidence
boundaries.
Talk with Zoiko Tech about the sector, jurisdictions, regulated activities, systems and
control or evidence requirements you need to support. We’ll route the discussion to the
relevant industry, solution, technology and trust context.