
Connect protection, identity and evidence without blurring who controls what.
Zoiko Tech connects cybersecurity, digital identity and access, and assurance/regulatory evidence through shared policy, governance, integration and proof boundaries — preserving the authoritative state, owner and maturity of each system.
Choose the trust question
Protection, access and proof require different authorities.
Protection / resilience
Security posture, responsible owner and recovery.
Identity / access
Subject, entitlement, delegation and policy decision.
Assurance / privacy
Source, scope, currentness and permitted data use.
Integration / diligence
Approved technical contracts and authoritative Trust routes.
Three technology planes
Distinct control planes connected through policy and evidence.
Cybersecurity
Protection, resilience and security operations.
Digital Identity & Access
Identity, authentication, entitlement and delegated authority.
Assurance & Regulatory Evidence
Governance, evidence and compliance infrastructure.
Cross-cutting privacy
Purpose, minimization and source-owned trust boundaries.
Shared trust architecture
Context $\rightarrow$ identity $\rightarrow$ authority $\rightarrow$ policy $\rightarrow$ action $\rightarrow$ signal $\rightarrow$ evidence.
Context & identity
Actor, resource, operating entity and authenticated context.
Authority & policy
Entitlement/delegation and actual allowed action.
Protected action & signal
Responsible system owns execution and observed state.
Evidence & recovery
Source, scope, freshness, accountable owner and next action.
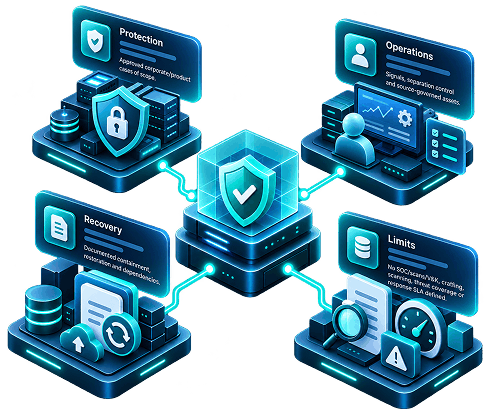
Cybersecurity & resilience
Architecture scope does not establish a complete security suite.
Protection
Approved corporate/product control scope.
Operations
Signals, responsible owner and source-governed state.
Recovery
Documented containment, restoration and dependencies.
Limits
No SOC/SIEM/XDR/MDR, staffing, scanning, threat coverage or response SLA inferred.
Digital Identity & Access
Authentication is not permission to perform every action.
Subject
Person/service identity at documented scope.
Authentication
Only approved actual method, no assumed SSO/MFA/biometrics.
Entitlement / delegation
Who may act, on whose behalf, within which scope.
Decision
Policy permit/deny/review state is separate from identity verification.
Assurance & regulatory evidence
Controls, review and certification are different claims.
Governance
Approved control objectives and owners.
Evidence
Source, period, applicability, freshness and limitations.
Review
Reviewer, decision, exception and supersession.
Claims
No guaranteed compliance, regulator approval or attestation without exact current evidence.
Threat detection & response
A signal is not a resolved incident.
Signal
Source-backed security-relevant observation.
Triage
Context and accountable assessment.
Response
Approved owner/action and explicit authority.
Outcome
Investigation, containment and recovery retain distinct definitive states.
Privacy & data protection
Privacy is a distinct control layer.
Purpose
Approved use and minimum necessary data.
Access
Actual role, resource and external-disclosure context.
Retention / jurisdiction
Only source-defined rules; no residency guarantee.
Privacy authority
Canonical policy and request routes; no duplicate unsupported promises.
Trust & compliance
Architecture summaries do not outrank their source.
Trust Center
Authoritative diligence and proof routing.
Security / Privacy
Source-owned practices and legal notices.
Disclosure / Status
Separate vulnerability reporting and live operational state.
Compliance boundary
Readiness, alignment, implemented controls and certification remain distinct.
State & evidence integrity
Each material state needs its owner and source.
Security
Alert, incident, investigation and recovery are not equivalent.
Identity / access
Subject identity, authentication and authorization are distinct.
Control / evidence
Implemented control is not independently verified compliance.
Freshness
Stale/out-of-scope/unknown evidence cannot appear current or approved.
Readiness-gated platform evidence
No named candidate is promoted as generally available.
Zoiko Shield
Finish / directory only when public-approved.
Zoiko iD / Zoiko Access
Build; exact methods and launch scope source-gated.
Zoiko Assure / ZoikoTax
Build; no filing coverage or compliance guarantee inferred.
Public exposure
Current maturity, owner, source and destination approval required.
Integration & developer layer
Only actual public contracts support implementation.
Interfaces
Approved APIs, SDKs and event definitions.
Authentication
Only documented protocol/scopes and permission semantics.
Evidence integration
Source-owned records and permitted metadata.
Readiness
No invented endpoints, identity network or technical guarantees.
Operational resilience & status
Unknown must not default to healthy.
Dependencies
Actual supported provider/system states.
Degradation
Explicit degraded, incident or unavailable state.
Status authority
Current service-health source; no hard-coded uptime.
Recovery
Approved action and escalation, with evidence retained under policy.
Implementation & modernization
Scope and verify control authority before expansion.
Map
Actors, resources, sources and definitive states.
Define
Policy, evidence and approved exceptions.
Validate / pilot
Denied, missing, stale, failed and partial states.
Expand
Only after security, capability, evidence and support readiness approval.
Technology in practice
Architecture proof needs attributable evidence.
Problem
Actual approved operational/control issue.
Deployment
Source-approved platform and integration scope.
Outcome
Evidence-backed result and limitations.
Evidence pending
No supplied customer records; no invented breach prevention, certification or compliance outcomes.
Clear answers about control and proof.
Does this establish a security product suite?
No. Cybersecurity scope is protection, resilience and security operations; exact tools require evidence.
Are SSO, MFA or verification methods available?
No specific methods are established in this source. Current approved exact tools require evidence.
Are these platforms generally available?
Shield is Finish; iD, Access, Assure and Tax are Build. Public exposure remains readiness-gated.
Does evidence prove compliance?
Only exact approved scope, authority and current evidence support a specific claim; no blanket guarantee.
Make control ownership inspectable.
Start with a bounded evaluation.
This is a local inquiry, not vulnerability intake. Canonical public disclosure and support routes require verification.
Trust Center preview